The entry into force of Royal Decree 933/2021 has brought data protection in the tourism sector into the spotlight. The requirement to collect and retain a large volume of sensitive information about travelers for three years has raised concerns among experts, who warn of privacy risks and potential penalties.
A disproportionate measure?
The data that must be recorded includes personal, financial, and contractual information, such as national ID numbers, addresses, credit card numbers, and email addresses. This volume of information, combined with the requirement to store it for three years, increases the likelihood of data breaches and misuse. Furthermore, some of this data—such as credit card numbers—is highly sensitive, which increases the risk of identity theft in the event of a security breach.
Without robust safeguards, the risk of losing control over personal data is very high. Furthermore, this regulation could violate fundamental principles of the GDPR (General Data Protection Regulation), such as the principle of data minimization, which requires limiting data collection to the minimum necessary to achieve the intended purpose.
Administrative Burdens and Legal Risks for Businesses
Data protection is not only a concern for travelers but also a challenge for businesses. The decree imposes a significant administrative burden, especially on small businesses and the self-employed, who must implement technological systems to properly record, store, and protect information.
These investments are not only costly but also complex to implement in companies with limited resources, which can lead to unintentional noncompliance and, ultimately, penalties.
Fines can be substantial. Noncompliance with the GDPR due to issues such as data breaches, security failures, or misuse of information can result in penalties of up to 20 million euros or 4% of the company’s annual revenue, whichever is greater.
In addition, the decree establishes specific fines forviolations related to passenger registration, ranging from 100 to 30,000 euros, depending on the severity.
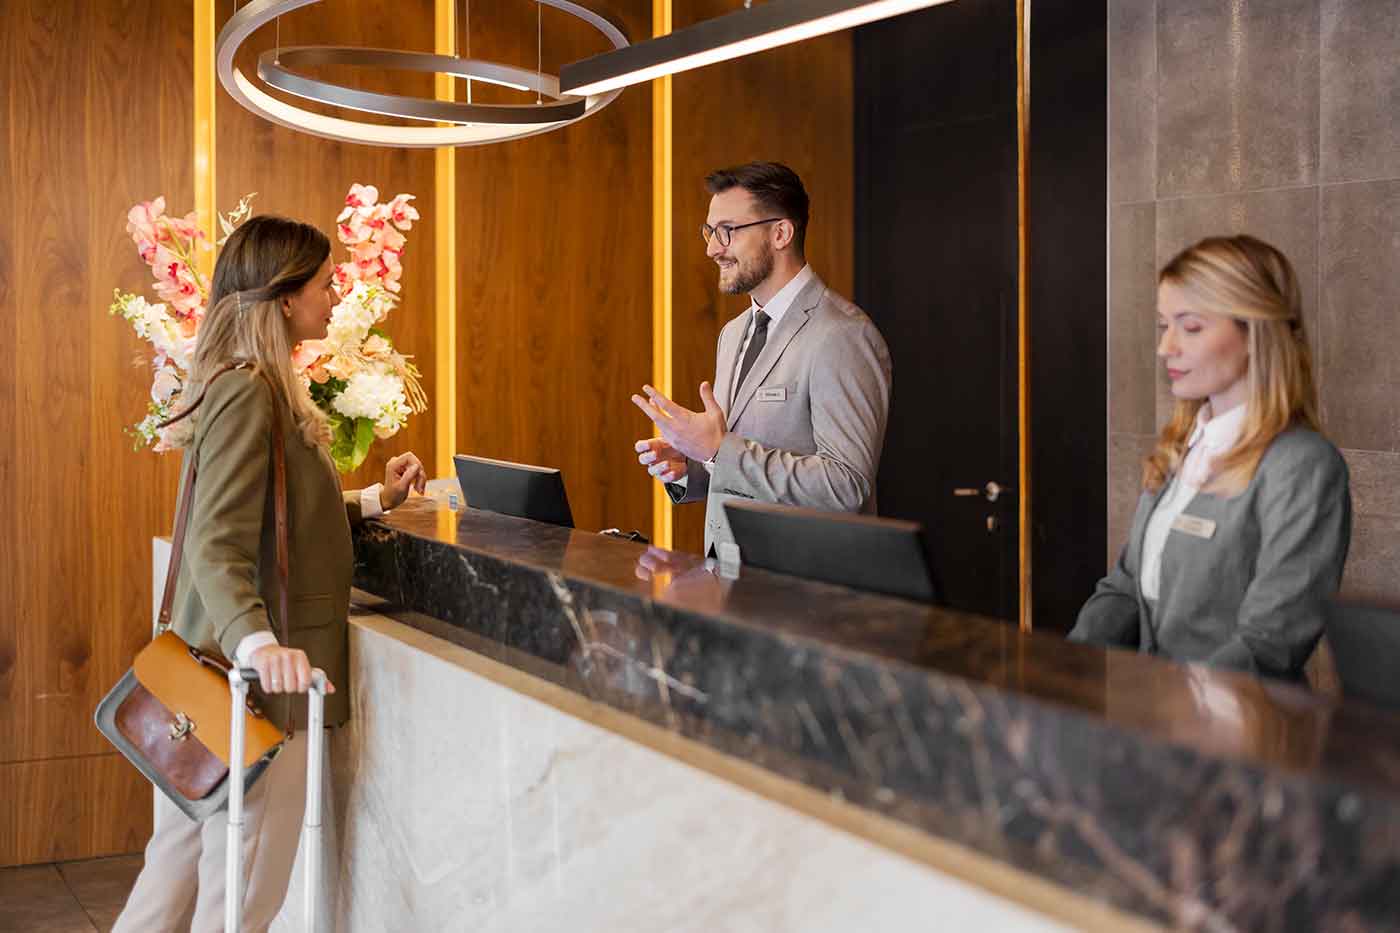
Equally important is the impact on day-to-day operations. Managing this data can slow down check-in processes, lead to conflicts with customers who refuse to provide additional information, and divert resources from other critical areas of the business. This is especially relevant in a highly competitive industry such as tourism, where any delay or problem can negatively affect the customer experience and, ultimately, the establishment’s reputation.
The Importance of Ensuring Data Proportionality
The precedent set by the Court of Justice of the European Union’s annulment of Directive 2006/24/EC, due to its indiscriminate nature, should serve as a warning. In the words of Ruth Benito, a data protection expert at Elzaburu: “The mass storage of personal data without proportionate measures or clear justification creates risks that may be irreversible for privacy.”
This scenario underscores the need to place data protection at the center of any measure involving the mass processing of personal information. Only a balanced approach—one that combines robust security safeguards with a clear and proportionate justification—will ensure both public safety and the fundamental rights of citizens. At the same time, it is crucial to protect the competitiveness of the tourism sector, one of Spain’s economic drivers.
Within this framework, companies must prepare to meet this challenge by investing in compliance and data protection systems that not only meet regulatory requirements but also strengthen travelers' trust.
Ruth Benito, Of Counsel. Privacy and Data Protection